


Continuous Mobile
AI Penetration Testing
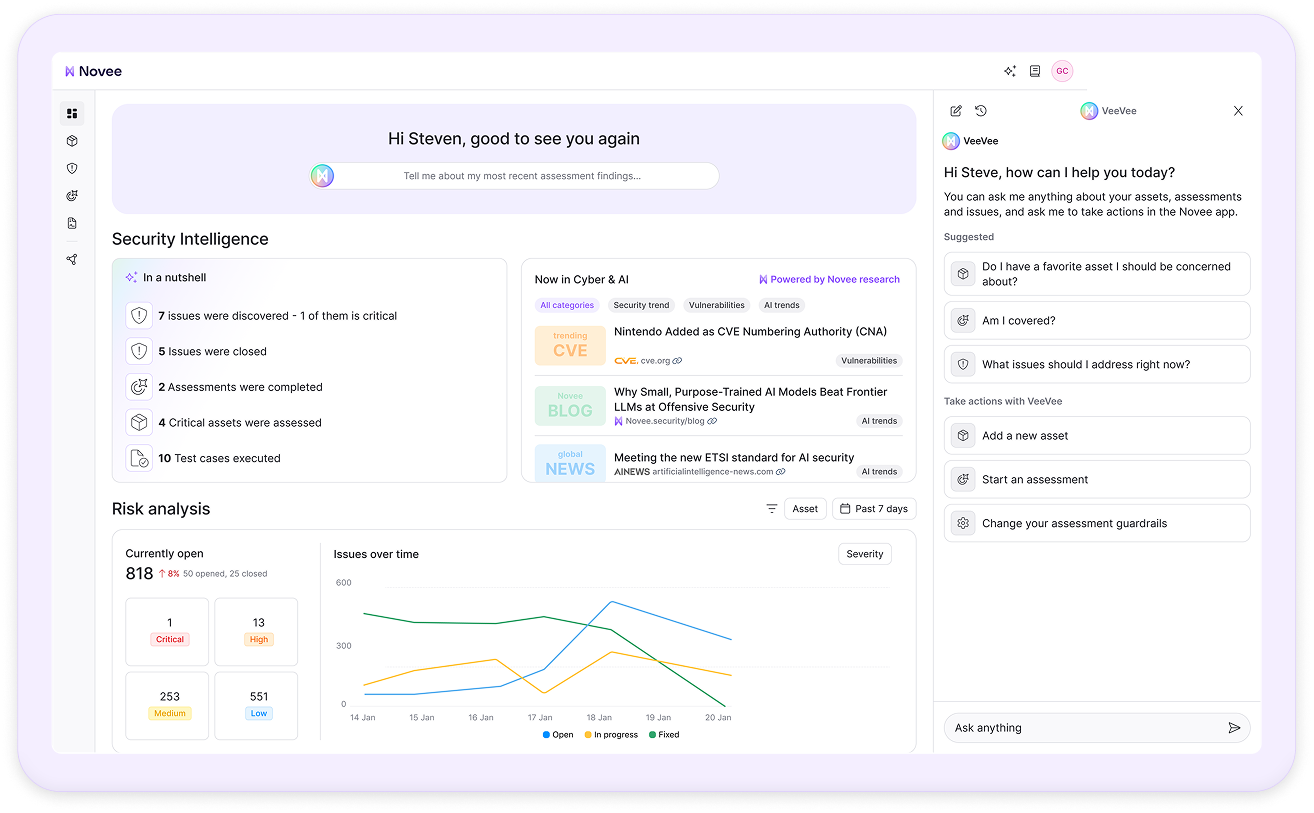
Novee brings the same continuous AI-powered penetration testing platform used for web applications to mobile apps.
Uncover vulnerabilities that lead to breaches, prove findings are exploitable, and close the loop with tailored remediation and automatic retesting.
THE OFFENSIVE TESTING GAP
Mobile Apps are a Primary Attack Surface. Annual Tests Can't Keep Up.
Mobile applications change with every release – new features, new APIs, new attack surfaces. Attackers don’t wait for your next testing cycle. Static penetration tests cover a single snapshot, then go stale until the next cycle. Every release shipped without testing is a window attackers can exploit.
Mobile apps are already the least-tested part of most security programs. The gap between how often they’re tested and how fast threats move gives attackers a clear path in.
THE SOLUTION
Novee’s Continuous Mobile Pentesting with Expert Depth
Novee operates like a continuous attacker that first understands your mobile applications – then systematically tests how they can be broken, proves exploitability, and guides fixes until risk is eliminated.
Continuous mobile testing
Always on and self-service – test on demand, no scheduling or toolchains required.
- Complete mobile attack surface coverage
- Change-triggered
- Combined APK and runtime testing
High-impact flaws, not just CVEs
Finds complex exploit chains and business logic vulnerabilities that scanners and shallow tools miss.
- Multi-step exploit chains
- Authorization gaps (BOLA, IDOR, BFLA)
- Compounding knowledge per app
Proven exploitability
Validates findings with a working exploit and reproducible steps – no false positives, no noise.
- Multi-agent validation
- Working exploit for every finding
- Python PoC + reproduction steps
Tailored fixes & retesting
Delivers precise remediation based on your architecture and retests automatically.
- Code-level fixes, not generic guidance
- WAF rules for your specific stack
- Auto-retest to confirm the fix held
Chosen by teams that take attackers seriously



What security leaders say
“As the leading agentic orchestration platform for the enterprise, data isolation between our customers is non-negotiable. We need to prove that continuously, not once a year. Novee adapted to our multi-tenant SaaS product within days.”
Scott Roberts
CISO

“Our pen tests took weeks and consistently missed critical issues. Novee found them immediately and gave us instant remediation guidance. It showed us what we'd been missing.”
John Barrow
CISO

“Novee rethinks penetration testing for how attacks actually happen today. Continuous, attacker-level validation that proves what’s exploitable and shows teams exactly how to fix it is a meaningful shift for modern security programs.”
Troy Wilkinson
Former Fortune 500 CISO

"The hardest vulnerabilities for us to catch aren’t misconfigurations or known patterns. They’re business logic issues that only show up when someone understands how the application is supposed to work. That’s exactly the gap Novee closes."
Tamir Ronen
CISO, HiBob

"We had EASM tools and manual pentests that produced mostly noise. Novee came in black-box with zero credentials and within days found dozens of real vulnerabilities we could actually fix."
Itzik Menashe
CISO, Global VP IT InfoSec & productivity

“As an AI researcher, what stood out about Novee is that they built a proprietary offensive AI model designed to think like an attacker, rather than wrapping generic LLMs. That matters for enterprise-grade results.”
Tal Shapira
PhD, CTO

“This was by far the deepest and fastest security assessment we’ve had. Novee uncovered issues across our web and mobile applications that had gone undetected before, and the level of depth was unlike anything we’d seen from other vendors.”
Amir Tito
CISO

“We had urgent compliance need and we couldn’t wait weeks for DAST findings, and an in-depth pentest report. Instead Novee came in and delivered immediate value with their AI pentesting platform; we closed our gaps and quickly met the criteria we needed for certification.”
Ron Reiter
CTO
"Traditional DAST produced either zero or irrelevant results. We needed something that could identify complex vulnerabilities like server-side request forgery. Novee consistently surfaces findings we simply weren't seeing before."
Robert Kugler
Head of Security, IT & Compliance

"Before Novee, we were getting a snapshot once a year. Now we have continuous coverage across our application portfolio, we're already finding things that prior manual pentests missed completely, and I have real confidence that our security posture reflects what's actually in our environment."
Abhijeet Patkar
Cyber Security Manager
NOVEE FOR MOBILE PENETRATION TESTING
Comprehensive Mobile
Security Coverage
Every entry point tested and every assessment mapped to OWASP MASTG.


ONE PLATFORM
Same platform as web app testing
- Unified risk tracking, issue management, and reporting
- Results in hours
- Full app attack surface coverage

SEAMLESS DEPTH
Complete mobile attack surface
- Every mobile entry point tested: Activities | Services | Deep Links | Content Providers | Intent | WebViews | Broadcast Receivers
- No setup or specialized tools
- Uncovers novel vulnerabilities

COMPLIANCE
Continuous, audit-ready evidence
- MASTG-mapped results for SOC 2, ISO 27001
- Meets customer due diligence
- Full OWASP MASVS Coverage
HOW IT WORKS
Offensive Al Reasoning Across
All Mobile Endpoints
Upload an APK and Novee handles the rest.
Our offensive AI combines static analysis, runtime testing, and deep mobile application context in a single assessment – continuously uncovering the vulnerabilities that lead to real breaches, proving exploitability, and guiding remediation.
Our offensive AI combines static analysis, runtime testing, and deep mobile application context in a single assessment – continuously uncovering the vulnerabilities that lead to real breaches, proving exploitability, and guiding remediation.

01
Discover
Continuous Coverage
Continuous coverage of the entire application attack surface (web apps, API, and mobile), tested the way an attacker would – by interacting with real flows, endpoints, and behavior to understand what’s actually exposed.
Test on demand or let Novee fire automatically when code ships.

02
Detect
ֿHigh-Impact Vulnerabilities
Understands how your application behaves and tests it for chained attack paths, business logic flaws, authorization gaps, and workflow manipulation that other tools miss.
Context compounds with every cycle, so testing gets deeper, faster, and more targeted over time.
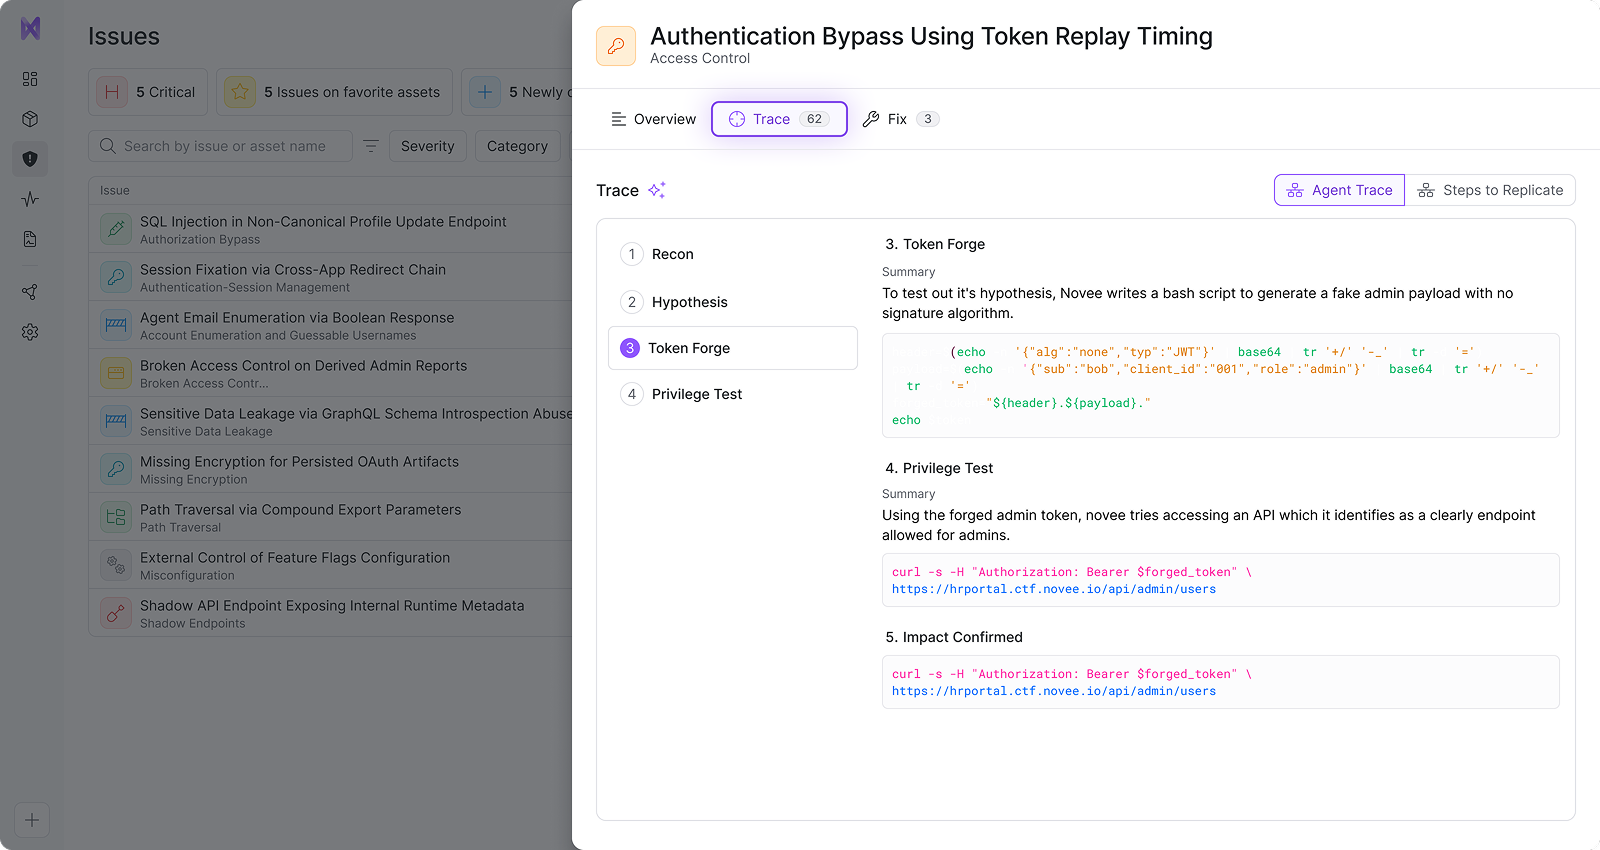
03
Validate
Proven Exploitability
Every finding is independently validated for exploitability, reproducibility, confidence, and real-world impact – complete with working exploits, reproduction steps, and PoC scripts.
Only proven vulnerabilities reach your team.
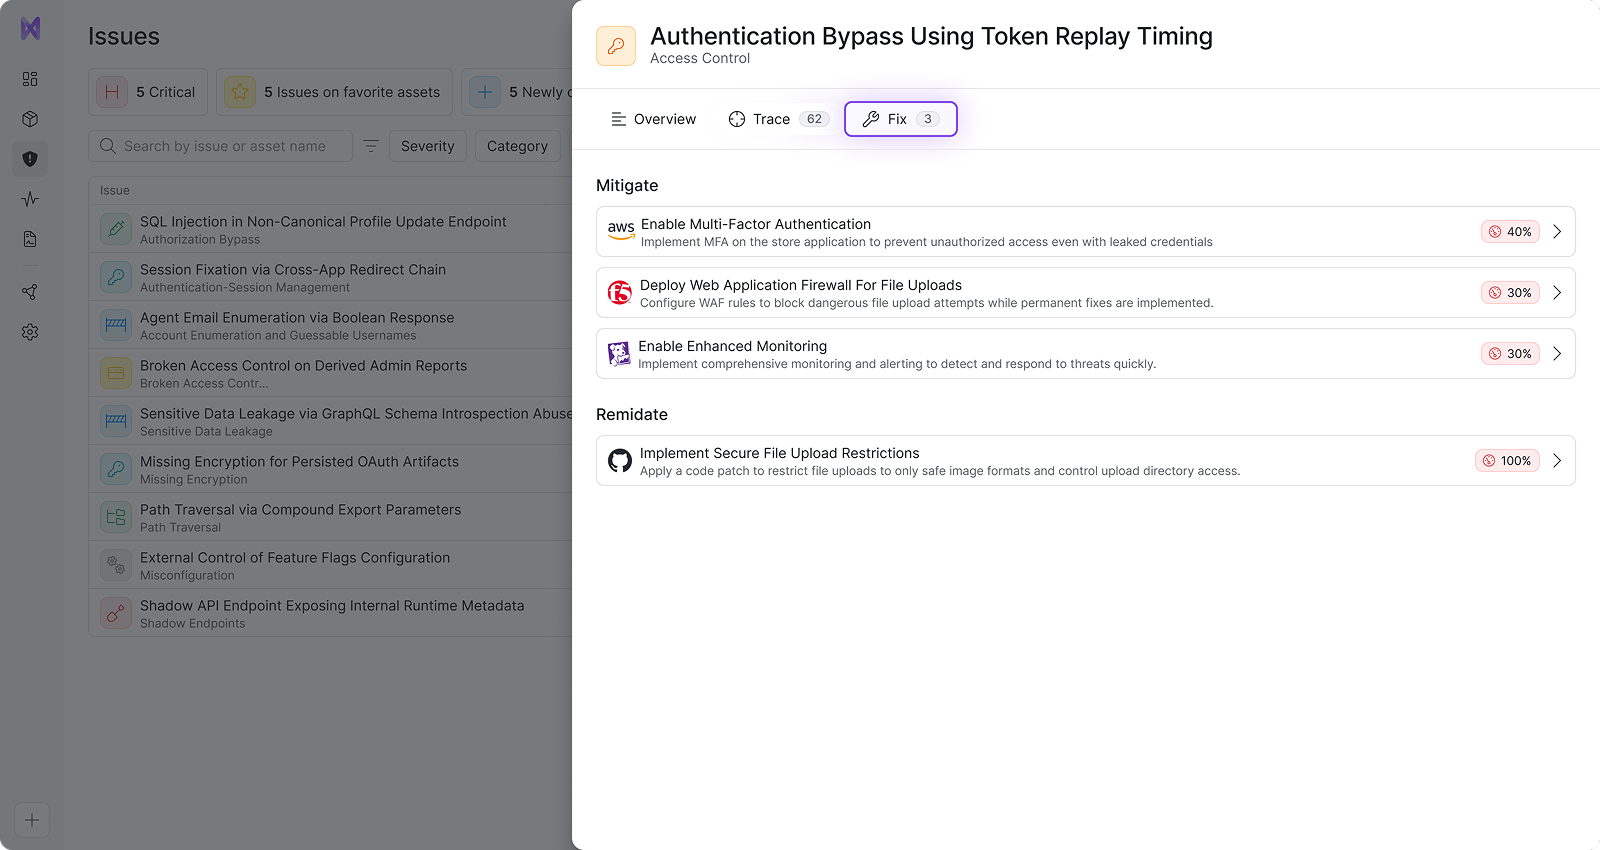
04
Remediation
Clear, Tailored Fixes
Get remediation guidance tailored to your specific WAF, backend, frameworks, and infrastructure – or route fixes directly to the AI coding agents your engineering team already uses via Agentic Fix.
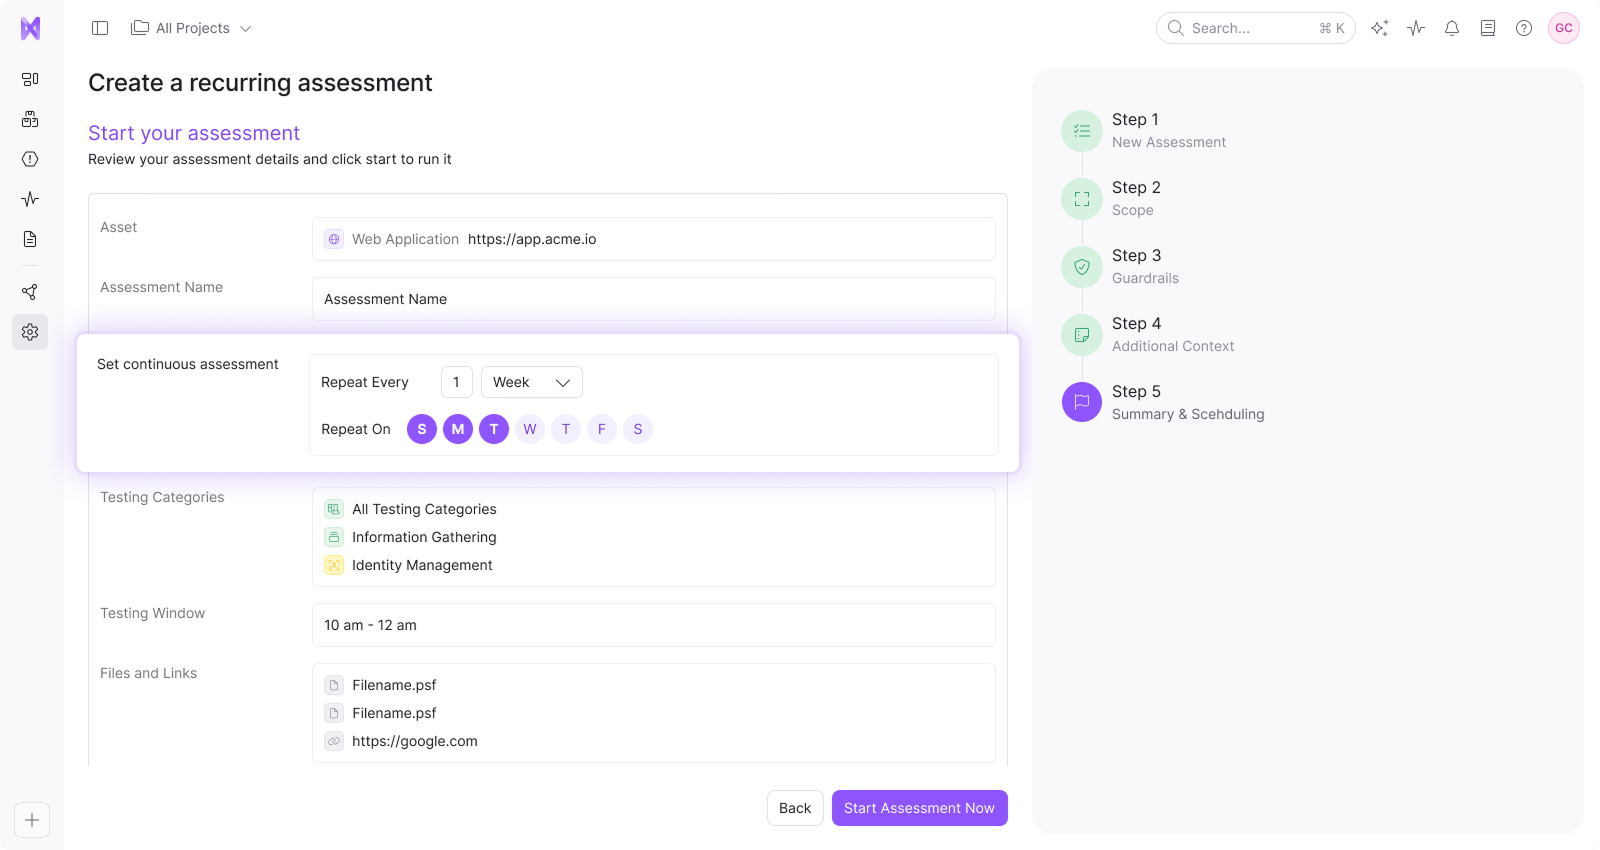
05
Repeat
Continuous Retesting
Automatically retests as code changes and environments evolve – learning from each cycle, so testing gets more targeted and effective over time.
The Novee System
Offensive AI Reasoning Across All Mobile Entrypoints
Our offensive AI combines static analysis, runtime testing, and deep application context in a single assessment - continuously uncovering the vulnerabilities that lead to real breaches.
Proprietary AI
Offensive System
Patent Pending
Continuously optimized for offensive security
Novee’s offensive AI agents combine our proprietary model, frontier models, and real attacker expertise to plan, pursue, validate, and remediate high-impact mobile vulnerabilities.
Continuously benchmarked, evaluated, and optimized as new models, attacker techniques, and applications evolve.

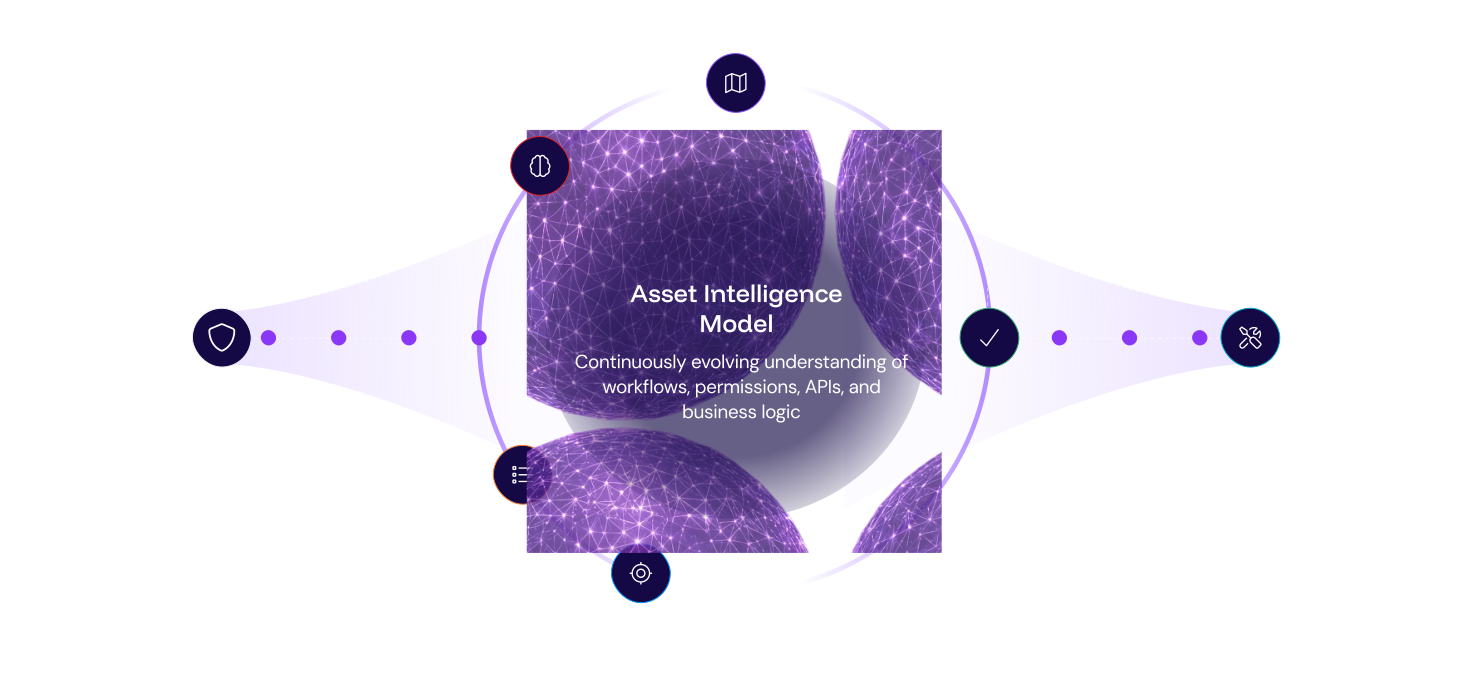
Asset intelligence
model
Understands how your applications work to power deeper testing
The Asset Intelligence Model continuously builds understanding of your mobile application’s workflows, permissions, APIs, business logic, and mobile components.
Context compounds over time, so testing gets smarter, more targeted, and coverage deepens with each cycle.


What makes Novee fundamentally different
A continuously optimized offensive AI engine – designed to find, prove, and fix real vulnerabilities, and improve as AI, attackers, and applications evolve.
Proprietary multi-model AI offensive system
Purpose-built offensive agents reason, adapt, and execute like real attackers – combining offensive tradecraft, adaptive orchestration, and the best AI for each task. Continuously benchmarked, evaluated, and optimized as AI, attacker techniques, and applications evolve.
Asset intelligence model
A persistent intelligence layer that understands the application’s workflows, roles, APIs, and business logic – enabling deeper, faster, and more targeted testing every cycle as context compounds over time.
Continuous offensive AI optimization
Rigorous scientific evaluation across real applications and exploit scenarios continuously improves offensive performance as attackers, applications, and AI evolve.
Multi-agent validation - no theoretical risk
Every finding is independently validated through exploit execution, blind re-testing, and verification before it reaches your team. Only proven vulnerabilities make it through.

