Case Study: Why UiPath’s CISO Swapped Point-in-Time Scans for Continuous Proof
When CISO Scott Roberts set out to prove the integrity of UiPath's multi-tenant SaaS environment, he wasn't looking for a once-a-year checkbox. He needed ongoing assurance that tenant isolation would hold up against the real attacker techniques his enterprise customers demand protection from.
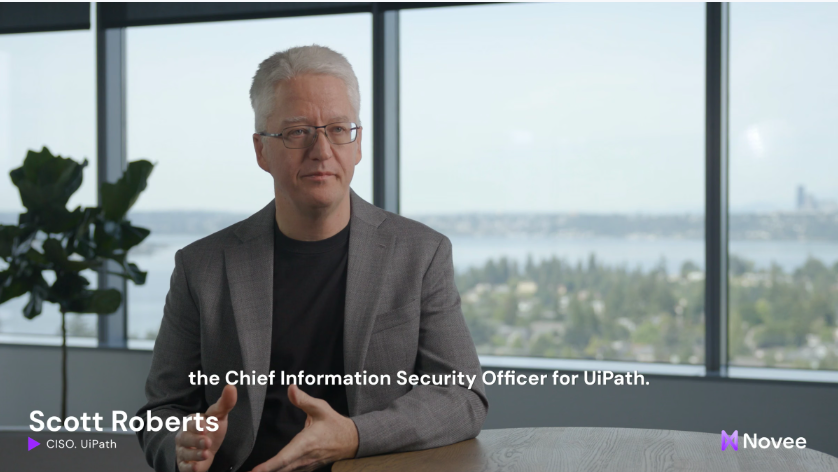
UiPath is the world’s leading business orchestration and automation platform, trusted by thousands of customers across the most heavily regulated industries to run mission-critical workloads, and hold their most sensitive data. As the first AI-powered business orchestration and automation platform certified for safe AI agents (according to the AIUC-1, the standard developed by the Artificial Intelligence Underwriting Company), UiPath operates at a scale and pace where security can’t be a point-in-time exercise.
When CISO Scott Roberts set out to prove the integrity of UiPath’s multi-tenant SaaS environment, he wasn’t looking for a once-a-year checkbox; he needed ongoing assurance that tenant isolation would hold up against the real attacker techniques his enterprise customers demand protection from.
Hear from Scott why he partnered with Novee, and what’s changed since.
The limitations of traditional vulnerability scanners
UiPath ships constantly, and its platform evolves faster than any quarterly testing cycle can capture. For Scott, the volume alone made point-in-time testing a non-starter.
“It is very important that we’re able to continually assess and monitor our environment, because it’s constantly changing. We did over 500 releases on our cloud platform last year. So it’s continually advancing, continually evolving, and with the speed of agentic automation, we have to keep up with the speed of our deployment capability.”
The tools his team had relied on couldn’t keep up. Worse, they buried the signal that mattered.
“Traditional scanners would generate tons of noise just based on open-source findings inside of the platform that really weren’t relevant in our environment.”
Penetration testing built for UiPath’s environment
What set Novee apart was that it took the time to learn how UiPath actually works before testing it, mapping the multi-tenant architecture and the way customers build workflows on the platform.
“Unlike the traditional scanners that operated on a one-size-fits-all approach, Novee actually took the time to understand our platform, understand our multi-tenant architecture, and understand how customers were building workflows in our environment – and, in a matter of days, reflect that environment within their product, and show us vulnerabilities being leveraged inside UiPath’s core business logic, to make sure that our customers were safe and secure.”
That depth is what surfaced flaws in business logic rather than in generic dependency lists, the kind a one-size-fits-all scanner will never catch.
The Novee platform delivers proof of exploitability that security can act on
A finding is only actionable if it’s real. Novee proved exploitability and gave both the security team and the engineers the exact path an attacker would take.
“Many vulnerability scanners will simply tell you there’s a potential vulnerability. What Novee was able to do was to verify independently that these vulnerabilities, even when chained together in complex attacks, were reachable inside of our platform, and lay out the exact path that an attacker might use – both to my security team and the engineers that need to address those issues. And again, not just from a generic open-source package point of view, but targeted and designed around the UiPath platform, taking our multi-tenancy into consideration, our authorization and access control systems into consideration, so that we’re able to really focus on the vulnerabilities that matter the most.”
Because Novee proved each vulnerability was reachable and chained them the way a real attacker would, Scott’s team could put their hours into exploitable risk rather than chasing false positives.
Continuous testing alongside leading AI audits
For an AI-powered platform like UiPath’s, where highly regulated customers automate their mission-critical workloads and hold their most sensitive data, continuous validation and assurance can’t wait for the next audit window.
UiPath’s industry-leading audits, such as AIUC-1, determine which risks can be exploited in the AI agent’s environment. Novee amplifies that by mapping the attack path that would lead to such exploitation, running continuously between those audit cycles.
That combination gives Scott’s team a live view of how agent risk could actually be reached, keeping pace with UiPath’s release velocity between assessments.
Novee becomes an extended part of the UiPath security team
At UiPath’s release cadence, a vendor that shows up once a quarter and leaves a report was never going to work; Scott needed a partner embedded in how his team ships.
“In our environment, we really needed a partner that was an extended part of our security team; that as we’re doing these hundreds of deployments a year, is constantly monitoring our deployments for any potential issues that might crop up.”
That partnership comes back to the promise UiPath makes to its own customers.
“As the leading agentic orchestration platform for the enterprise, data isolation between our customers is non-negotiable. We need to prove that continuously, not once a year. Novee adapted to our multi-tenant SaaS product within days and now gives us ongoing validation that our tenant isolation holds up against real attacker techniques. That level of assurance is what our customers expect of us, and it’s exactly what we give them through this partnership.”
For Scott, the result is testing that finally operates at the level UiPath requires.
“Novee operates at the depth that our platform demands. Real-world findings. Zero noise.”
See for yourself the continuous offensive and defensive cybersecurity platform that proves real exploitability and automatically retests every fix. Get a demo.