
Novee Agentic Fix
Agentic remediation that turns every validated finding into a verified fix
Novee generates stack-specific remediation briefs and lets you route them to the AI coding agents you already use – then re-tests to verify the risk is closed.
Chosen by teams that take attackers seriously



You can find risk in minutes. Fixing it still takes weeks.
Autonomous pentesting compresses discovery from quarters to hours, but fixing still means triage, validation, handoffs, patching, and manual re-testing. The window between finding and fix stays wide open.


The remediation backlog
Findings arrive faster than fixes
Continuous testing surfaces validated findings around the clock, but every one still has to be triaged, assigned to engineering, and explained before code is fixed.

Generic guidance slows remediation
Fixes without attack context
Most tools hand off boilerplate references and leave engineers to reverse-engineer the real problem, so patches address the symptom and miss the root cause.

Unverified patches refill the backlog
A closed ticket isn’t closed risk
Most workflows never re-run the original exploit, so teams can’t be sure a vulnerability is resolved, and findings cycle back into the queue on the next test.
CAPABILITIES
Turn every validated finding into a verified fix, fast and at scale
Novee Agentic Fix turns every validated exploit into precise remediation guidance for the AI coding agents your developers already use – then re-tests the original attack to verify the vulnerability is resolved.
Briefs built from the real exploit
Every brief includes the entry point, affected code paths, and attack vector Novee validated.
- Stack-specific fixes
- Context is preserved from finding to fix
Fixes routed to your AI agents
Route remediation briefs to tools your engineers use like Claude, Copilot, Codex, or Cursor.
- Github-native handoff
- Preserve developer workflows
Automatic re-assessment
Novee re-runs the original exploit to confirm the vulnerability is resolved without new risk.
- Runs automatically when PR lands
- Verifies risk is actually closed
PERSONAS
Built for teams that want to close the loop fast on risk
Remediation lives between security and engineering.
Agentic Fix gives each side what it needs to close findings for good.

CISO
Close the remediation window
See what was found, what was fixed, and what Novee verified — proof that real risk is actually going down.
- Proven exploitability
- Fixed and verified, not just found
- Evidence for the board and audits

AppSec
Hand off fixes without missing context
Route remediation briefs to the agents engineering already uses, with the full exploit context attached.
- Every finding ships with a working exploit and PoC script
- No manual replay of transcripts
- Fixes tied to the affected code paths

Engineer
Fixes arrive as a pull request, with your stack in mind
Remediation lands in the repo as a PR, grounded in the real attack — no security jargon to decode.
- Guidance for your actual codebase
- Root cause, not the symptom
- Re-tested before it’s closed
HOW IT WORKS
How Novee works: From validated finding to verified fix
Novee operates like a continuous attacker that first understands your application, systematically tests how it can be broken, proves exploitability, and then drafts detailed remediation guidance for your coding agents.
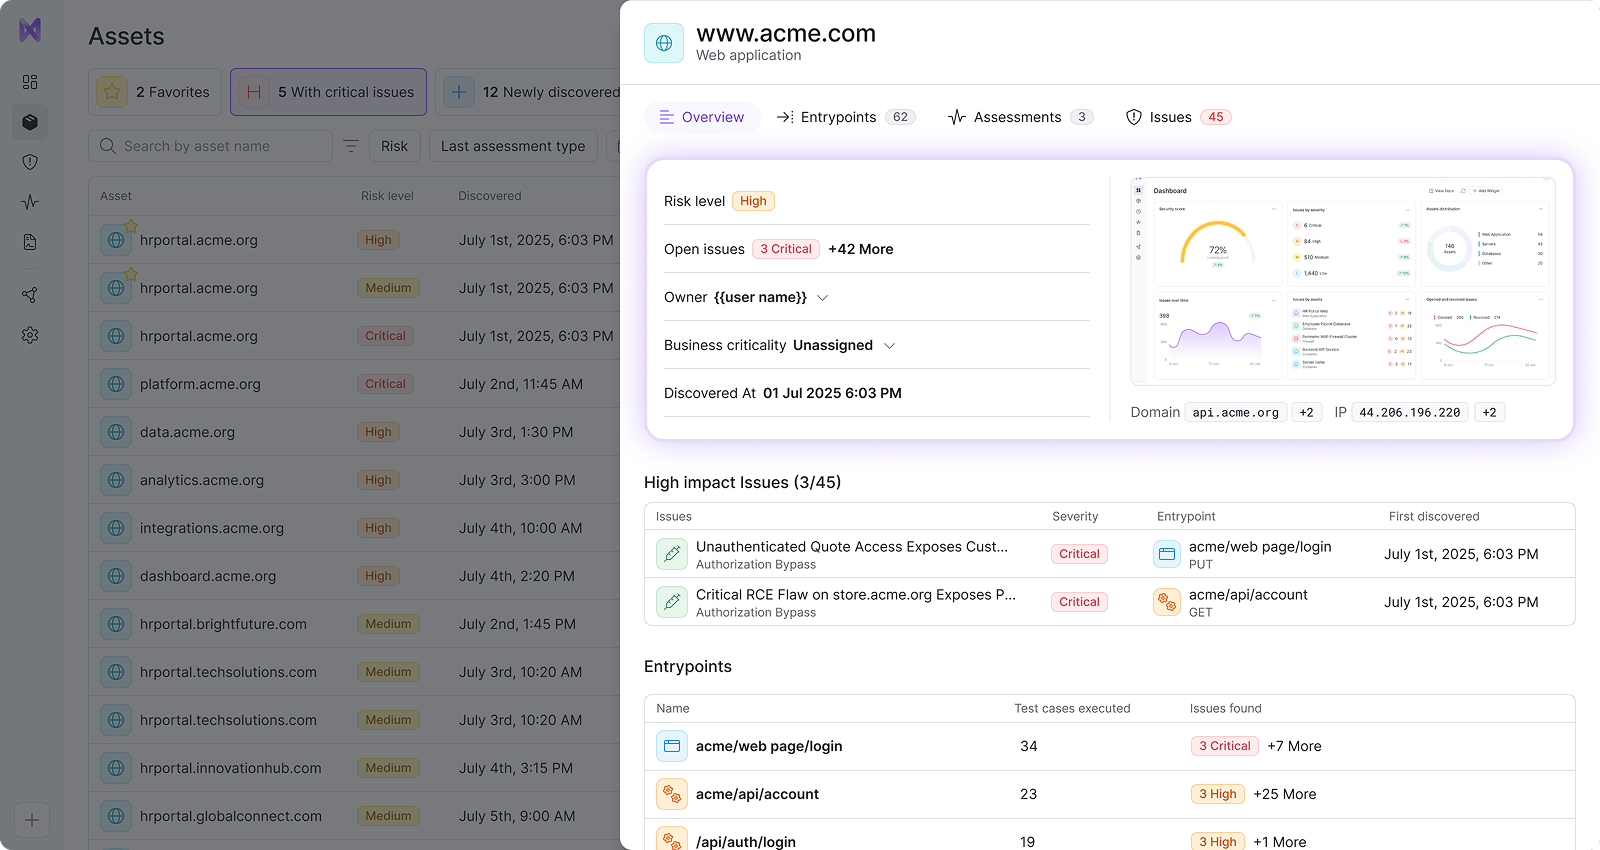
01
Discover
Continuous Coverage
Continuously map your live environment the way an attacker would – by interacting with real flows, endpoints, and behavior to understand what’s actually exposed.
Test on demand or let Novee fire automatically when code ships.
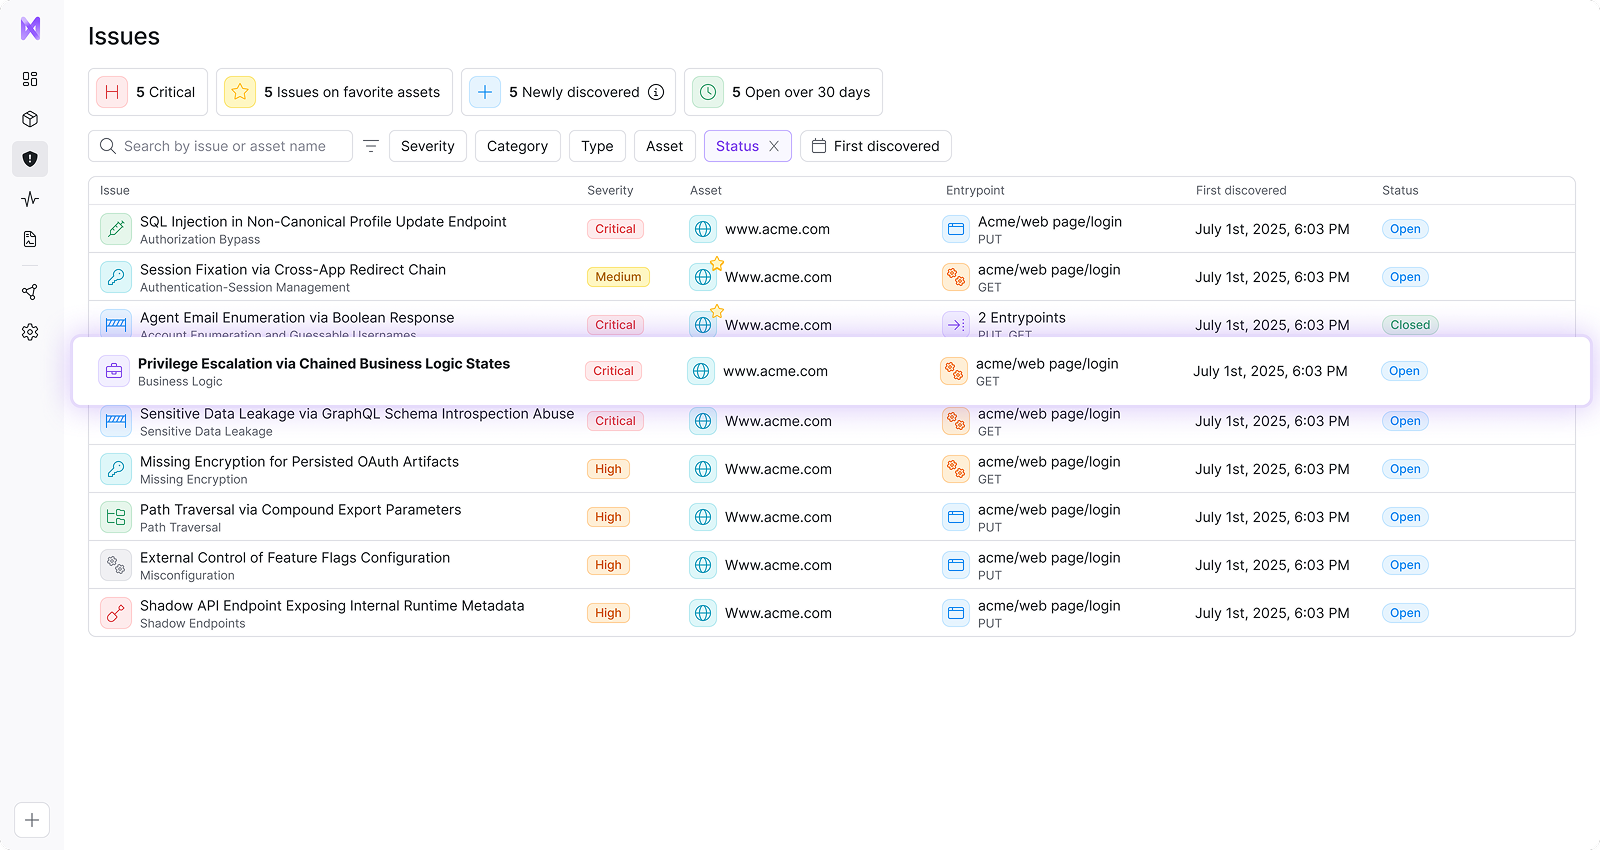
02
Detect
ֿHigh-Impact Vulnerabilities
Understands how your application behaves and tests it for chained attack paths, business logic flaws, authorization gaps, and workflow manipulation that other tools miss.
Context compounds with every cycle, so testing gets deeper, faster, and more targeted over time.
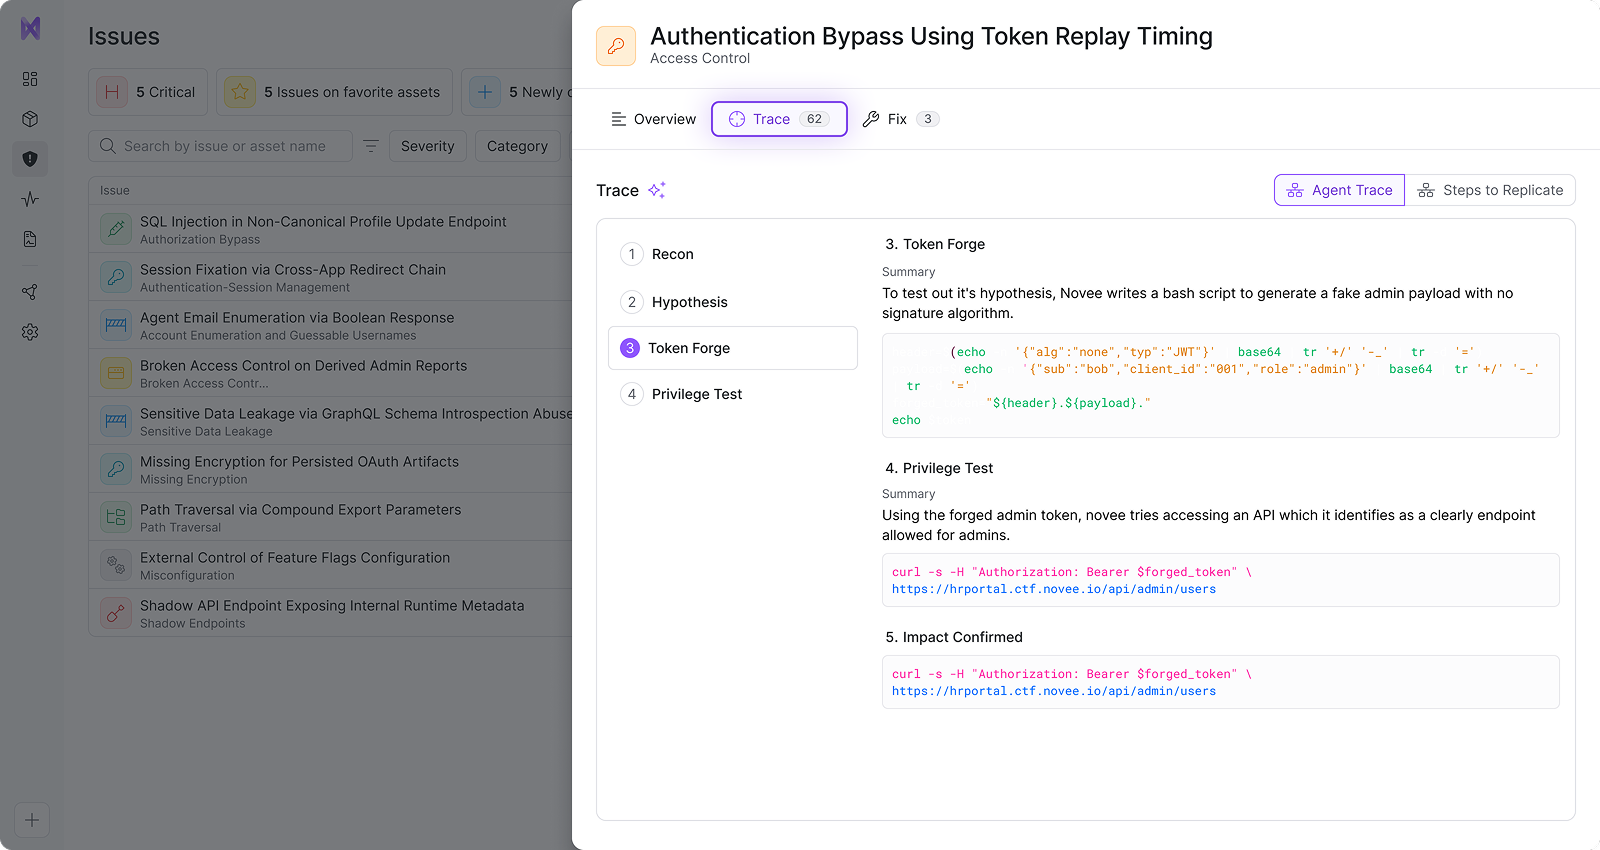
03
Validate
Proven Exploitability
Every finding is independently validated for exploitability, reproducibility, confidence, and real-world impact – complete with working exploits, reproduction steps, and PoC scripts.
Only proven vulnerabilities reach your team.
04
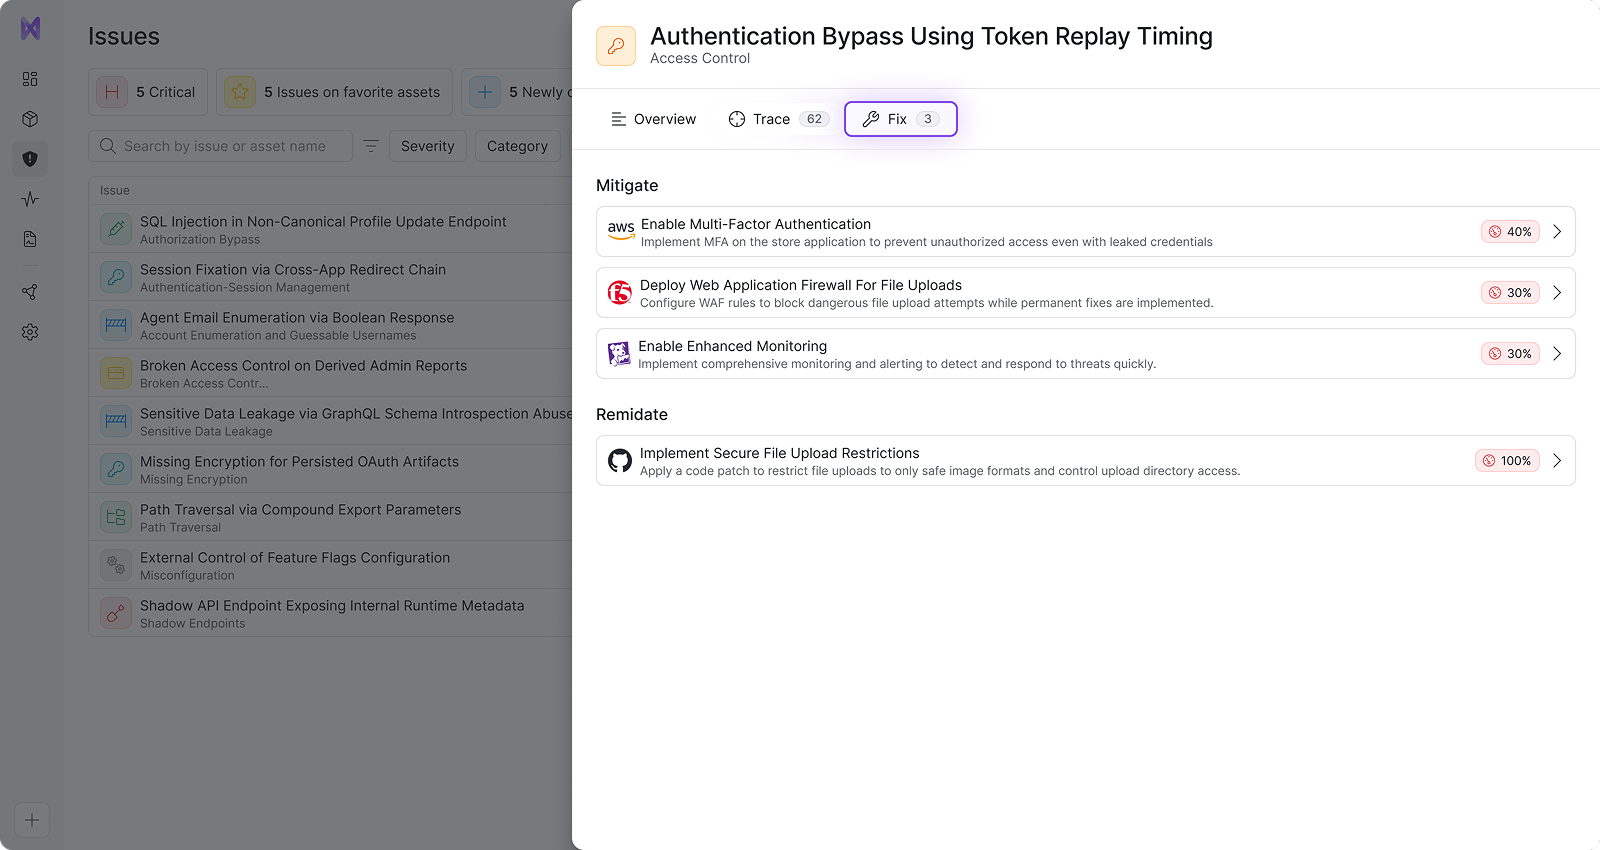
Remediation
Clear, Tailored Fixes
Get remediation guidance tailored to your specific WAF, backend, frameworks, and infrastructure – or route fixes directly to the AI coding agents your engineering team already uses via Agentic Fix.
05
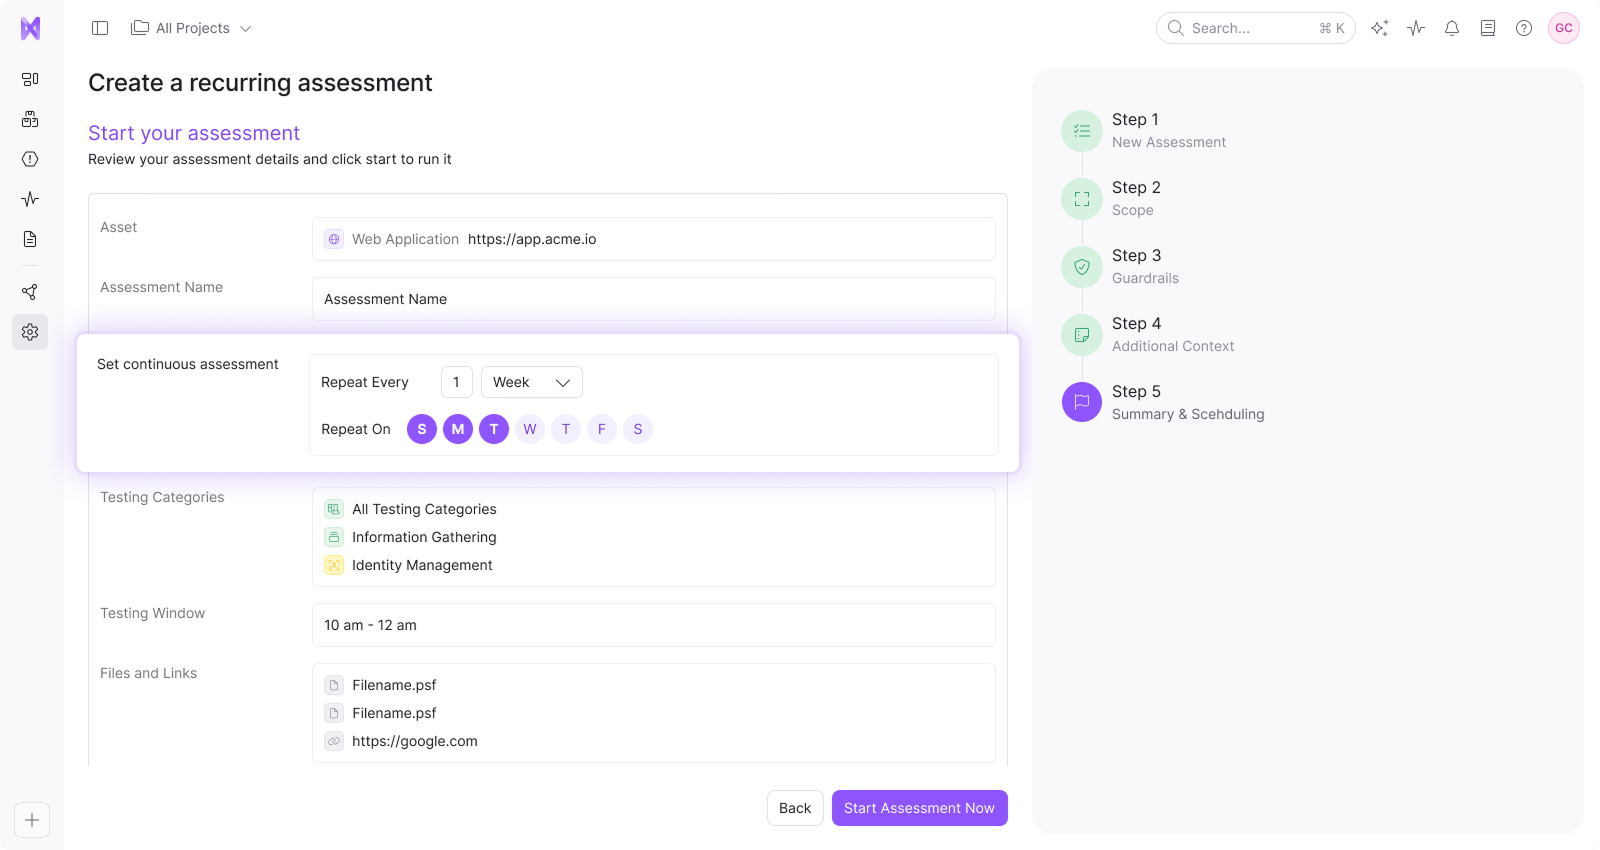
Repeat
Continuous Retesting
Automatically retests as code changes and environments evolve – learning from each cycle, so testing gets more targeted and effective over time.
What security leaders say
“As the leading agentic orchestration platform for the enterprise, data isolation between our customers is non-negotiable. We need to prove that continuously, not once a year. Novee adapted to our multi-tenant SaaS product within days.”
Scott Roberts
CISO

“Our pen tests took weeks and consistently missed critical issues. Novee found them immediately and gave us instant remediation guidance. It showed us what we'd been missing.”
John Barrow
CISO
“Novee rethinks penetration testing for how attacks actually happen today. Continuous, attacker-level validation that proves what’s exploitable and shows teams exactly how to fix it is a meaningful shift for modern security programs.”
Troy Wilkinson
Former Fortune 500 CISO

"The hardest vulnerabilities for us to catch aren’t misconfigurations or known patterns. They’re business logic issues that only show up when someone understands how the application is supposed to work. That’s exactly the gap Novee closes."
Tamir Ronen
CISO, HiBob
"We had EASM tools and manual pentests that produced mostly noise. Novee came in black-box with zero credentials and within days found dozens of real vulnerabilities we could actually fix."
Itzik Menashe
CISO, Global VP IT InfoSec & productivity
“As an AI researcher, what stood out about Novee is that they built a proprietary offensive AI model designed to think like an attacker, rather than wrapping generic LLMs. That matters for enterprise-grade results.”
Tal Shapira
PhD, CTO
“This was by far the deepest and fastest security assessment we’ve had. Novee uncovered issues across our web and mobile applications that had gone undetected before, and the level of depth was unlike anything we’d seen from other vendors.”
Amir Tito
CISO
“We had urgent compliance need and we couldn’t wait weeks for DAST findings, and an in-depth pentest report. Instead Novee came in and delivered immediate value with their AI pentesting platform; we closed our gaps and quickly met the criteria we needed for certification.”
Ron Reiter
CTO
"Traditional DAST produced either zero or irrelevant results. We needed something that could identify complex vulnerabilities like server-side request forgery. Novee consistently surfaces findings we simply weren't seeing before."
Robert Kugler
Head of Security, IT & Compliance
"Before Novee, we were getting a snapshot once a year. Now we have continuous coverage across our application portfolio, we're already finding things that prior manual pentests missed completely, and I have real confidence that our security posture reflects what's actually in our environment."
Abhijeet Patkar
Cyber Security Manager
"Novee takes the complexity out of penetration testing while providing transparent, step-by-step details of everything they do. Novee delivers the attacker-level validation we need to confidently close real external-domain exposures that other testing misses."
Anthony Gacayan
Senior Information Security Engineer
"Novee has become our main security testing system because they focus on the product itself, where most of our real risk sits and where other tools keep coming up short. With regulatory pressure building across our global markets, continuous, change-triggered penetration testing has become essential."
Ronen Rabinovich
Sr. Manager Product Security Lead
The Novee System
Offensive execution guided by
deep asset understanding
Most tools scan for patterns or rely on humans. Novee combines both – AI that thinks like attackers, grounded in deep application understanding.
Proprietary AI
Offensive System
Patent Pending
Continuously optimized for offensive security
Purpose-built for offensive security testing. Combines Novee’s proprietary model, frontier models, real attacker tradecraft, and adaptive orchestration into continuously optimized offensive agents.
Continuously benchmarked, evaluated, and optimized as new models, attacker techniques, and applications evolve.
Asset intelligence
model
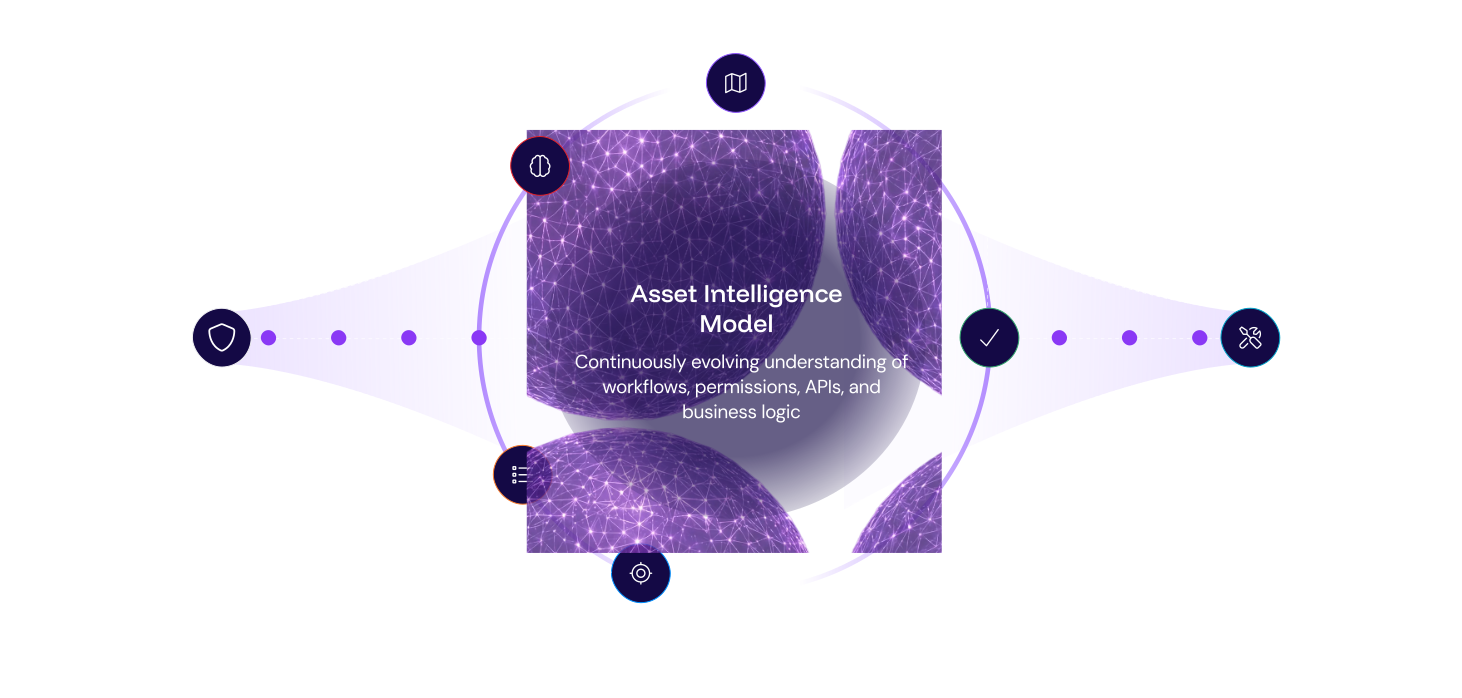
Understands how your applications work to power deeper testing
Builds a living model of your environment – capturing workflows, roles, APIs, and business logic to power deeper discovery, more accurate validation, and more precise remediation.
Context compounds over time, so testing gets smarter, more targeted, and coverage deepens with each cycle.
HOW NOVEE STAYS AHEAD
The Novee Gym: Better Exploit Intelligence. Better Remediation.
The Novee Gym continuously evaluates and optimizes the offensive AI that finds and proves vulnerabilities – creating stronger exploit intelligence to guide remediation and verify risk closure.

Proprietary Model + Multi-Model Routing
Novee combines its proprietary offensive model with leading frontier models, intelligently routing each task to the best performer.

Purpose-Built Offensive Security Harness
Specialized agents, tools, and orchestration work together to discover, exploit, and validate complex vulnerabilities.

Continuous Benchmarking + Optimization
The Novee Gym continuously evaluates the full offensive AI system against real applications to improve overall performance.