Attackers don’t limit themselves to the applications you’re already testing. They look for anything exposed to the internet – forgotten subdomains, staging servers left online, and infrastructure your team may not even know exists. When a critical new CVE emerges, they look for ways to exploit it, often chaining multiple weaknesses into a larger attack.
Attackers see one environment with multiple ways in. But most security teams still rely on separate tools to discover external assets, validate exposures, and test applications.
Today, we’re introducing Novee External Surface Testing, extending our AI pentesting platform beyond known applications to the entire internet-facing environment.
Novee discovers known and unknown external assets, tests newly disclosed CVEs and findings from third-party EASM tools, and validates what’s actually exploitable. It also uncovers new vulnerabilities and chained attack paths that individual scans can miss.
And when an asset needs deeper investigation, teams can move directly into full application pentesting, carrying findings and context forward – all in one platform.
Find the Unknown Unknowns
Your external attack surface is constantly changing. New applications go live, teams spin up staging environments, companies acquire new domains, and old infrastructure gets forgotten.
But just because an asset isn’t in your inventory doesn’t mean an attacker can’t find it.
Novee helps you find those unknown assets, starting with just your company name or domain. From there, it discovers your web applications and APIs, mail servers, file transfer and remote access services, VPN gateways, management consoles, underlying infrastructure, and other exposed services and entry points you may not know exist. Simultaneously the platform tests newly disclosed CVEs and findings imported from third-party EASM tools against live assets to confirm exploitability, maximizing the signals you already have and looking for the critical paths attackers like to take.
You review and confirm what’s yours before testing begins, giving your team visibility into assets that may have been missing from your security testing program.
Go Beyond Discovery. Prove the Risk.
Finding exposed assets is important, but an inventory alone doesn’t tell you which ones actually put your organization at risk.
Traditional EASM tools help teams discover and monitor internet-facing assets. But knowing what’s exposed isn’t the same as knowing what’s exploitable. Security teams are often left with long lists of potential vulnerabilities to investigate and validate themselves.
Novee goes beyond discovery to offensive testing.
Powered by our proprietary offensive AI, External Surface Testing maps your external environment, builds context across assets and services, and actively tests for vulnerabilities. It tests newly disclosed CVEs and findings imported from third-party EASM tools against live assets, validates exploitability, and uncovers new vulnerabilities and chained attack paths that traditional scanners miss.
Instead of relying on exposure scores or theoretical risk, Novee delivers prioritized, validated findings backed by evidence that shows:
- Which external assets have exploitable vulnerabilities
- Which leaked credentials are still valid
- Which newly disclosed CVEs pose a real, exploitable risk
- How vulnerabilities can be chained into more complex attack paths
- Which issues pose the greatest risk and deserve attention first
The result is a clear picture of real, exploitable risk, so security teams can focus on what matters instead of investigating every potential exposure.
How External Surface Testing Works
Getting started doesn’t require credentials, agents, or software installation. You can begin with a domain and let Novee expand the discovery.
The process is straightforward:
- Choose your starting point. Discover assets from a domain, import EASM findings, or select newly disclosed CVEs.
- Approve your scope. Review and confirm which assets can be tested.
- Test from the outside. Novee investigates vulnerabilities and chained attack paths without credentials.
- See proven risk. Get prioritized, validated findings backed by evidence and remediation guidance.
- Go deeper. Promote important hosts into full application pentests, carrying findings and context forward.
Testing can run on a schedule, helping teams keep up as their external environment changes.
Go Broad and Deep In One Platform
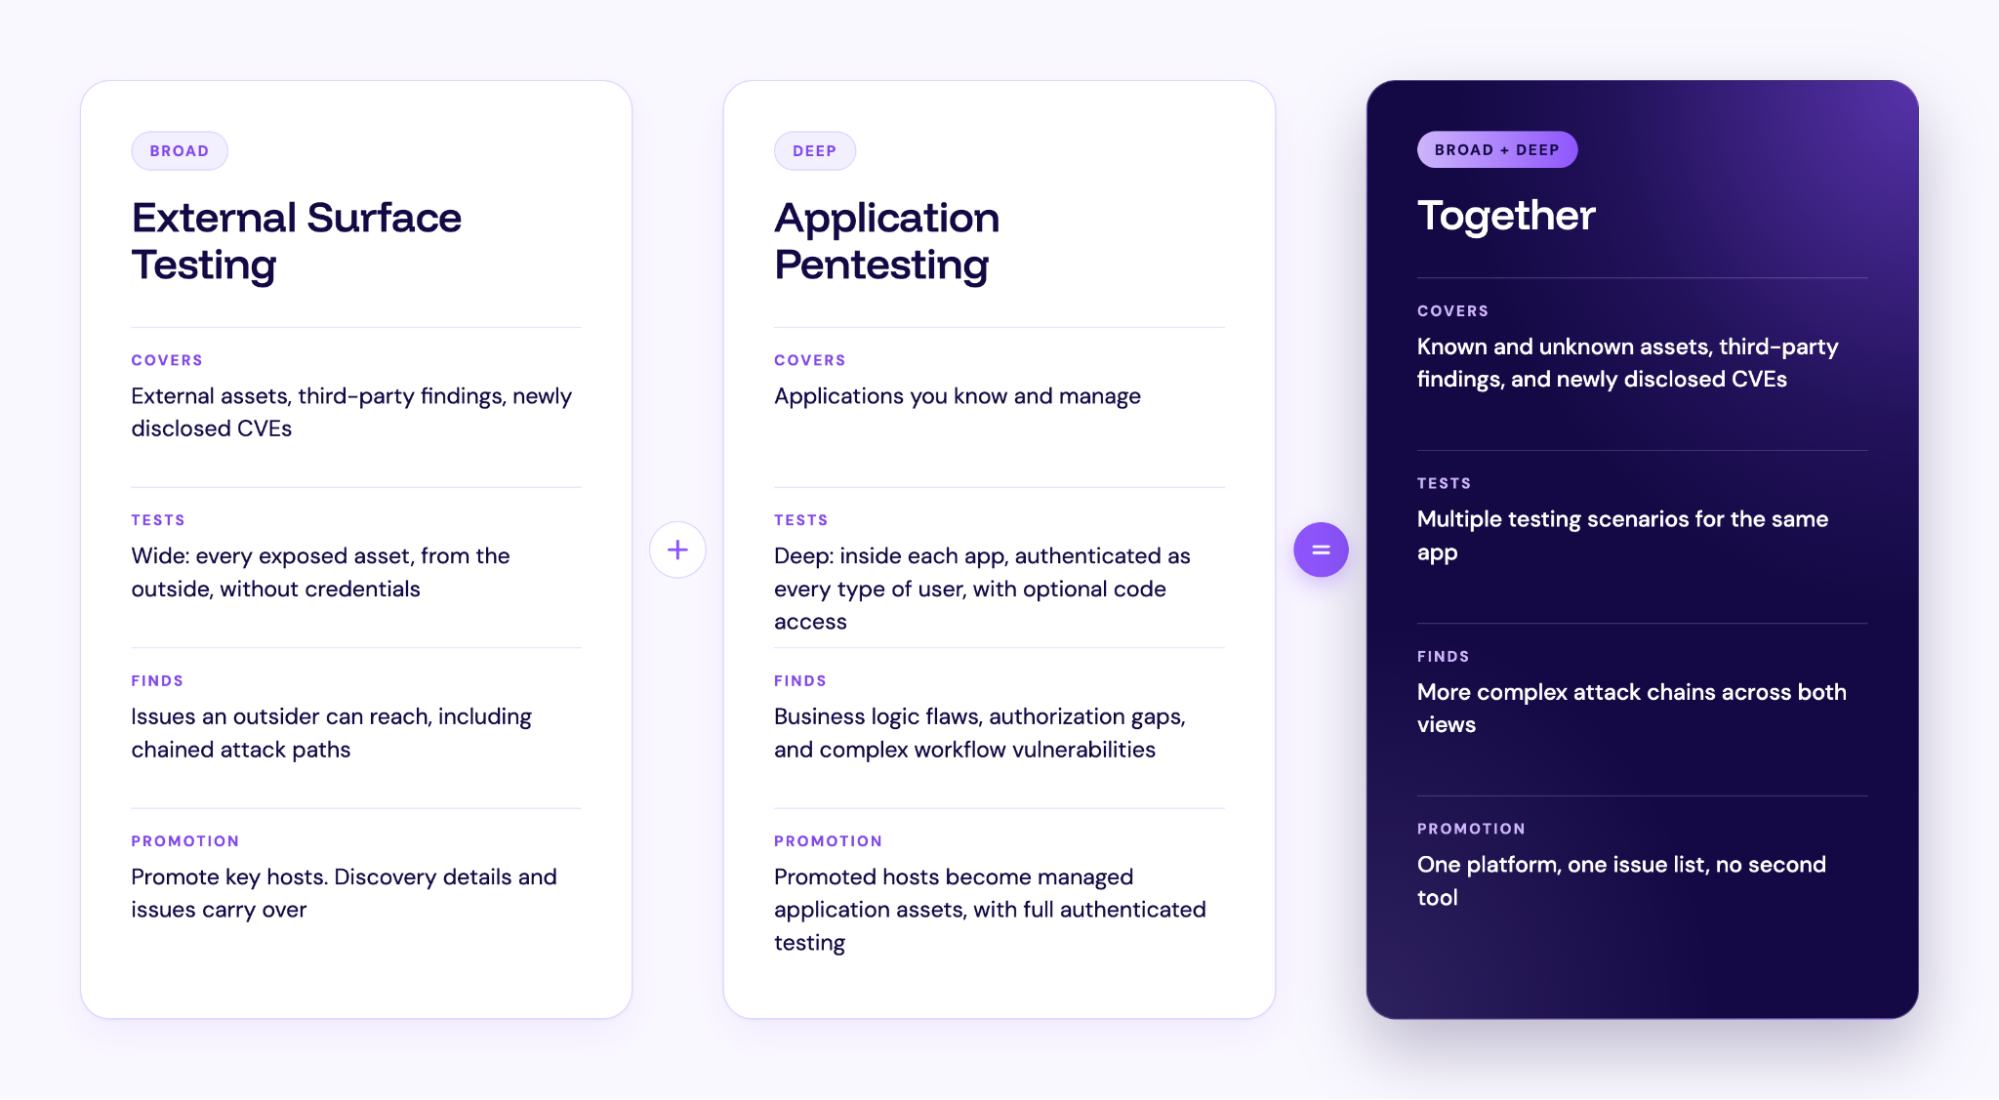
External Surface Testing and Application Pentesting answer two different questions.
- External Surface Testing shows what an attacker can discover, reach, and exploit from outside your environment – including unknown assets, exposed services, and newly disclosed CVEs.
- Application Pentesting goes deeper into known applications, testing authenticated workflows, roles, permissions, business logic, and complex attack paths.
Together, they give security teams broader coverage and deeper insight into exploitable risk. When an external asset needs further investigation, teams can promote it into a full application pentest, carrying discovery context and findings forward. All validated issues appear in one unified view, without switching tools or starting over.
By combining both approaches in one platform, Novee gives security teams a more complete picture of what attackers can actually exploit.
Built for Safe, Controlled Testing
Testing an entire external environment requires control over what gets tested and how.
External Surface Testing is designed with safeguards that let security teams expand coverage without losing control:
- Approved scope: Teams confirm ownership of discovered domains and IP ranges before testing begins.
- No credentials or installation: Testing runs from the outside, without requiring access to internal systems.
- Non-destructive testing: Novee validates vulnerabilities without destructive payloads or actions.
- Controlled traffic: Testing respects configured limits to reduce operational impact and unnecessary security alerts.
These controls make it practical to test more of your external environment while maintaining clear boundaries.
See Your Environment the Way Attackers Do
Attackers don’t distinguish between known applications, forgotten assets, and exposed infrastructure. They look for whatever they can exploit.
Novee brings that same outside-in perspective to security testing, combining broad external discovery, offensive validation, and deep application pentesting in one platform.
Because attackers see one environment. Your security testing should too.
Book a demo to see External Surface Testing in action.