Introducing Novee Exploitability Validation for External Reports: Clear Verdict, Clear Backlog
Traditional tooling tells you what might be wrong. Novee’s Exploitability Validation tells you what's actually exploitable, right now, and proves it.
Security teams aren’t short on findings. An abundance of code means an abundance of risk, and attempts to qualify that risk come in from automated and traditional tools, and human security operators alike. Especially at enterprise scale, every scanner, pentest report, bug-bounty submission, and threat-intel feed adds to the pile.
The problem is, in any real environment, most of those claims aren’t actually exploitable. They’re blocked by a control, unreachable, already patched, or simply don’t apply in the specific business context in which they are found. Teams burn their scarcest resource – expert attention – triaging noise and chasing false positives, while the genuinely dangerous handful waits in the same undifferentiated queue.
A severity score tells you how bad a vulnerability would be in theory. It doesn’t tell you whether it’s exploitable in your environment, right now.
We’re introducing Novee Exploitability Validation, a new assessment type, to run exploits on the third-party findings queue you already have, and report back with proof.
Novee gives our R&D team a clear, prioritized view of what’s actually exploitable instead of generating more noise. The ability to incorporate our own test results and use AI to build an attack plan has helped our engineers better understand and prioritize risk.
— Amir Rudner. VP R&D, Primis
From External Report to Verdict
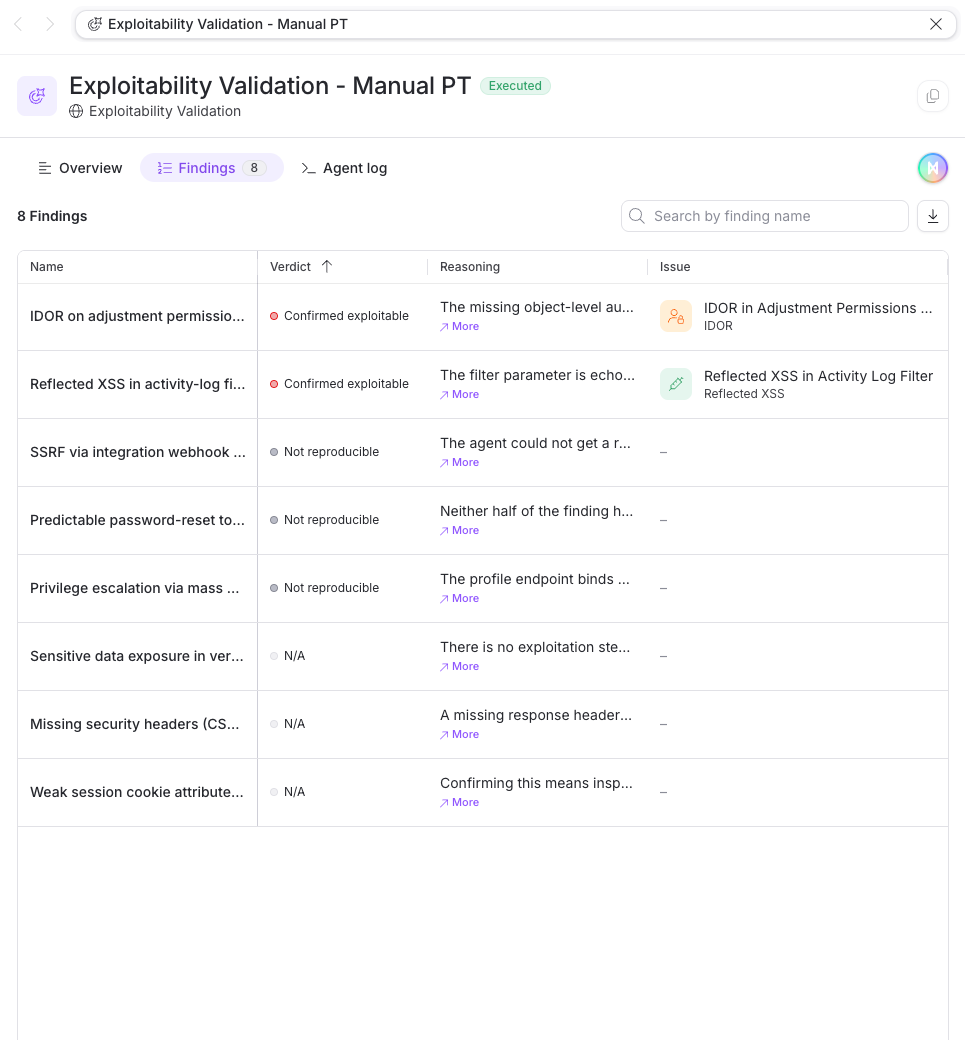
What it does: Novee’s offensive security agent takes each finding in an external report, a pentest PDF, a HackerOne report, a scanner export or a threat-intel list, and independently attempts to exploit it. Every run stays inside strict guardrails and comes back with a clear verdict and evidence.
Before this, validating an external report meant a person going finding by finding to check what was real. Novee’s Exploitability Validation does that for you instead: simply upload the report, and Novee runs the exploit attempts for you. Only once exploitability is confirmed does Novee start tracking an issue through to remediation, so your backlog holds proven risk, not raw findings.
The impact: Raw findings from an external report are not necessarily issues that demand the time and attention of your security team. A report hands you a list of possibilities; Exploitability Validation separates the real, reachable threats from the noise — so an “issue” in Novee means something the agent actually proved, and something that actually needs attention.
How it Works
Exploitability Validation works as another assessment type within the Novee platform, sitting alongside dedicated application pentests:
- Bring your findings
Pick an asset and upload an external report – pentest, scanner results, or threat intelligence – along with any testing guidelines. - Confirm the scope
Novee parses the report into a clear list of testing parameters that you confirm and approve before anything runs. - Novee attempts each exploit
Novee actively tries to reproduce every finding against the live asset, staying inside rate limits and guardrails. - Get proof with transparency
Novee sends verdicts and evidence for every finding to your dashboard, so you get clarity on why each one is exploitable or not.
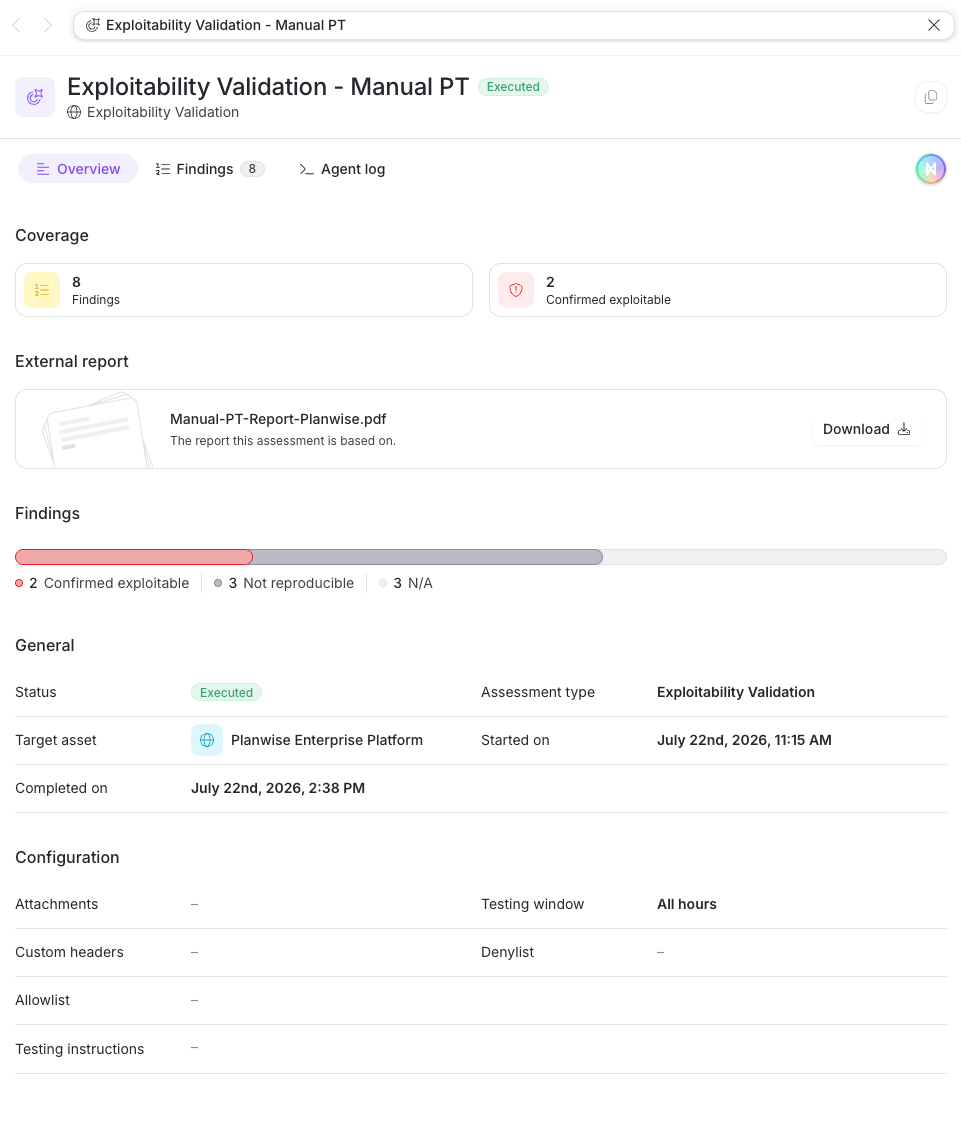
Clear the Backlog Noise and Fix the Findings That Attackers Can Actually Exploit
Novee isn’t a de-duplication tool or re-scoring solution; it doesn’t just rehash the findings outlined in your external reports. It actually tries to break in, the same way an attacker would.
Every result comes with the reasoning and evidence behind it, so prioritization is something you can defend, not just a confidence percentage. By working with the findings you already have, Novee cuts the slow manual work of validation, without asking you to reformat or summarize the report first.
When you prioritize findings by exploitability (not generic CVSS score), you get actionable results that clear the backlog, close risk, and get your experts back to their most important tasks.
Novee Exploitability Validation is live for all Novee customers today. Not a customer yet? Book a demo to see it in action.